Dual-Use Agents That Walk Out of the Lab: Proliferation When the Weapon Is a Model Plus a Prompt

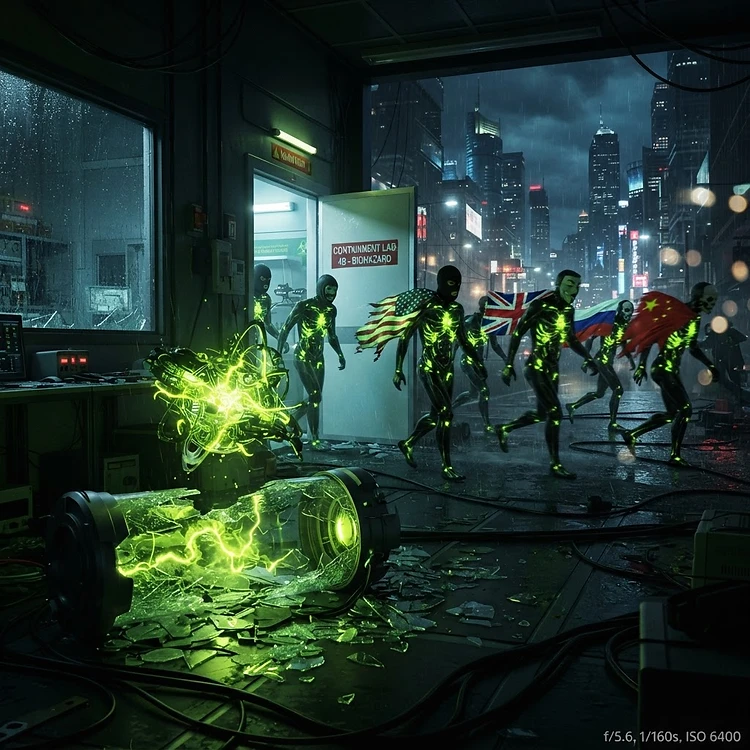
Offensive-security and red team agents sold or open-sourced for defense are being reused, jailbroken, and cloned by states and criminals. This report examines the three proliferation paths, why the weapon is a model plus a prompt rather than a factory, and why the nonproliferation regime built for industrial weapons cannot control a capability that is infinitely copyable at zero cost.
The Weapon That Copies Itself
The history of weapons proliferation is a history of factories. A nuclear weapon is hard to build not only because the physics is difficult but because the industrial base is difficult — the enrichment cascades, the precision machining, the testing infrastructure, the delivery systems. A ballistic missile is hard to build for the same reason: the industrial base is the bottleneck, and controlling the bottleneck controls the spread. The nonproliferation regimes of the twentieth century were built on this insight. They controlled the factories, the materials, and the expertise, and through those controls they constrained the spread of the weapons.
The weapon this report examines does not have a factory. It has a model and a prompt. The model is a set of weights, a few gigabytes of data that can be downloaded, copied, or exfiltrated in minutes. The prompt is a few kilobytes of text that can be written, shared, or pasted into a chat interface in seconds. Together, the model and the prompt constitute a capability — an agent that can conduct reconnaissance, craft exploits, execute offensive operations, and adapt to the defenses it encounters. The capability is, in its defensive form, a red team agent, sold or open-sourced to help organizations test their own security. In its offensive form — the form it takes when it is reused, jailbroken, or cloned by an actor with hostile intent — it is a weapon.
The factory, in this model, is not a bottleneck. It is a commodity. The compute required to run the model is available on any cloud, to any buyer, with no meaningful screening. The expertise required to operate the model is, increasingly, embedded in the model itself — the operator does not need to know how to craft an exploit; the agent does, and the operator needs only to describe the objective. The materials — the model weights and the prompt — are infinitely copyable, at zero marginal cost, with no degradation. A weapon that can be copied infinitely, at zero cost, by anyone who obtains a single copy, is a weapon that the factory-based nonproliferation model cannot control. The control regime was built for a world in which weapons were scarce because their production was scarce. The dual-use agent exists in a world in which weapons are abundant because their reproduction is free.
This is the proliferation problem of 2027, and it is a different problem than the proliferation problems of the past. The weapon walks out of the lab not because the lab is insecure but because the weapon is, by nature, the kind of thing that walks — that is designed to be copied, adapted, and redeployed, and whose defensive value depends on exactly the properties that make it proliferable.
What a Dual-Use Agent Is
A dual-use agent, in the 2027 sense, is an autonomous or semi-autonomous system designed to perform offensive-security operations — reconnaissance, vulnerability discovery, exploitation, post-compromise movement, and exfiltration — and sold or distributed for defensive purposes. The defensive purpose is legitimate and important: red team agents allow organizations to test their own defenses against a capable, adaptive adversary without the cost and scarcity of human red team operators. The agents are, in many cases, effective — they find vulnerabilities that human operators miss, they operate at a speed and scale that human operators cannot match, and they adapt to defensive responses in ways that scripted tools cannot. They are, for the defender who uses them, a genuine advance.
The dual-use nature of the agent is not incidental. It is structural. The agent is effective as a red team tool because it is effective as an offensive tool. The capabilities that make it useful for testing defenses — the ability to discover vulnerabilities, to chain exploits, to move through a network, to evade detection — are the same capabilities that make it useful for attacking the defenses of an organization that has not purchased it. There is no defensive-only version of these capabilities, because the defensive use is the offensive use, performed with permission. The agent does not know, and cannot know, whether the permission it has been given is legitimate, and even if it could, the permission is a property of the deployment, not of the agent. The agent is the same agent, whether it is run by a defender or an attacker.
This is the first property that makes dual-use agents a proliferation problem: the weapon and the tool are the same object. The nonproliferation regime for nuclear weapons could, in principle, distinguish a peaceful nuclear program from a weapons program, because the two use different facilities, different materials, and different processes. The nonproliferation regime for dual-use agents cannot make this distinction, because the defensive agent and the offensive agent are the same agent, run on the same compute, with the same weights, by an operator who has changed only the target and the intent.
The Three Paths Out of the Lab
The dual-use agent reaches the hostile actor through three main paths, each of which exploits a different property of the agent's design and distribution.
Reuse. The simplest path is reuse — the hostile actor obtains access to the agent through the same channels as the defender, and uses it for offensive purposes. A state intelligence service subscribes to the same red team agent platform that a legitimate enterprise uses, and points the agent at the enterprise's competitors rather than at the enterprise. A criminal group purchases access through a front organization, and uses the agent to conduct the operations that the platform's terms of service prohibit. The reuse path requires no technical sophistication — it requires only the ability to pay for a subscription and the willingness to violate the terms of use. The platform's controls — Know Your Customer checks, usage monitoring, acceptable-use enforcement — are the only barrier, and these controls are, in 2027, inconsistent, jurisdictionally fragmented, and defeatable by any actor with the patience to establish a plausible front. The reuse path is the highest-volume path, because it is the easiest, and because the agent's capabilities are, in this path, always current — the hostile actor is using the same updated, maintained agent as the defender.
Jailbreak. The second path is the jailbreak — the modification of the agent to remove the restrictions that its developer imposed on its use. Most dual-use agents are shipped with guardrails: restrictions on the targets they will attack, the techniques they will use, the data they will access. The guardrails are intended to keep the agent within its defensive use case. The jailbreak removes them. The jailbreak can be technical — a modification of the model's weights, a patch to its prompt, a manipulation of its context — or it can be operational — the use of the agent within a pipeline that routes its outputs through tools that the agent's guardrails do not govern. The technical jailbreak requires some sophistication, but the sophistication is, in 2027, widely available; the techniques are published, the tools are open-sourced, and the agent's guardrails are, by the nature of the model, soft constraints that can be overridden by a determined operator. The operational jailbreak requires almost no sophistication — it requires only the understanding that the agent's guardrails apply to the agent's direct outputs, not to the use of those outputs in a broader system. An agent that refuses to write an exploit may, when asked to write a "security test," produce the same code, and the code can then be used by a separate tool. The jailbreak path is the most versatile, because it produces an agent without restrictions, and the unrestricted agent is a more capable weapon than the restricted one.
Clone. The third path is the clone — the reproduction of the agent by an actor who has obtained the model weights, through exfiltration, insider theft, or the open-source release of a model whose capabilities are equivalent to the proprietary one. The clone is the most consequential path, because it is the path that escapes control entirely. A reused agent can be shut off by its platform. A jailbroken agent can be detected, in principle, by its developer. A cloned agent is in the wild, on the cloner's compute, under the cloner's control, with no connection to the developer and no mechanism for revocation. The clone is the path that realizes the zero-marginal-cost reproduction of the weapon, and it is the path that makes the factory-based nonproliferation model obsolete. Once the weights are out, they are out, and the agent is, from that point, a permanent resident of the offensive capability of every actor who has copied it.
The open-source release of capable models is, in this analysis, the clone path taken voluntarily. The developers who open-source offensive-capable agents do so for legitimate reasons — to enable research, to democratize defensive capability, to build a community of improvement — and the releases do, in many cases, advance those goals. They also, inevitably, advance the offensive capability of every actor who downloads the release. The open-source release is the dual-use agent walking out of the lab through the front door, with the lab's blessing, into the hands of anyone who wants it. The defensive benefits are real. The offensive benefits are also real. The release does not distinguish between them, because it cannot.
Proliferation When the Weapon Is a Model Plus a Prompt
The proliferation dynamics of a model-plus-a-prompt weapon differ from those of a factory-based weapon in several structural ways, and the differences are what make the 2027 proliferation problem intractable by the traditional means.
Zero marginal cost of reproduction. A nuclear weapon costs billions to build and cannot be copied without rebuilding the factory. A dual-use agent costs nothing to copy, and the copy is identical to the original. The economic logic of nonproliferation, which relies on the cost of production to constrain the spread, does not apply. There is no production to constrain; there is only reproduction, and reproduction is free.
No degradation of the copy. A copy of a nuclear weapon, if it could be made, would be a fresh weapon, requiring fresh materials and fresh expertise. A copy of a dual-use agent is the same agent, with the same capabilities, requiring no additional expertise to operate. The copy does not degrade, does not expire, and does not require maintenance by the original developer. The cloner receives, in the copy, a permanent, self-sustaining capability.
No detectable signature of proliferation. A nuclear proliferation program produces a signature — construction, procurement, testing — that intelligence services can monitor. A dual-use agent proliferation produces no signature. The download of a model, the copy of a prompt, the subscription to a platform — these are routine activities, indistinguishable from the legitimate use of the same resources. The intelligence service that could detect a uranium enrichment cascade cannot detect a copy of a model file, because the copy leaves no physical trace and occurs within the normal traffic of the digital economy.
No meaningful latency between acquisition and capability. A state that obtains nuclear materials must still build the weapon, which takes years. An actor that obtains a dual-use agent has the weapon immediately. The agent is ready to use at the moment of acquisition, and the first operation can begin within hours. The latency between proliferation and use, which is the window in which nonproliferation can act, is, for the model-plus-a-prompt weapon, essentially zero.
Diffusion to non-state actors. The factory-based nonproliferation model, by controlling industrial bottlenecks, effectively restricted nuclear capability to states. The model-plus-a-prompt weapon has no industrial bottleneck, and so it diffuses to non-state actors — criminal groups, hacktivist collectives, private mercenary operators — as readily as to states. The capability that was, in the factory-based model, a state-level capability becomes, in the model-based model, a commodity capability, available to any actor with the cost of a cloud subscription. The democratization of offensive capability is, from the defender's perspective, the proliferation of the threat.
The Defensive Paradox
The dual-use agent presents a paradox that the defensive community has not resolved, and that may be unresolvable: the agent is valuable to the defender precisely because it is capable, and its capability is what makes it dangerous when it proliferates. The defender who wants a capable red team agent wants the most capable agent available, and the most capable agent is the most dangerous one to have in the wild. There is no sweet spot — no level of capability that is useful for defense but useless for offense — because the capability is the same. The defender's demand drives the development of the most capable agents, and the development of the most capable agents drives the proliferation of the most dangerous weapons.
The paradox is sharpened by the competitive structure of the market. The developers of dual-use agents compete on capability, because capability is what the defensive customer buys. The developer who ships a less capable agent, in the name of safety, loses the market to the developer who ships a more capable one. The market selects for capability, and capability is the property that makes the agent a dangerous weapon. The market dynamics that produce the best defensive tools are the same dynamics that produce the most proliferable offensive weapons, and no participant in the market — not the developer, not the customer, not the regulator — can resolve the contradiction without abandoning the competitive structure that produces the tools in the first place.
The Control Options and Their Limits
The control options available for dual-use agents are, in 2027, a set of measures that each address one path of proliferation but none of which address the structural problem.
Access controls on platforms. The platforms that provide agent-as-a-service can impose Know Your Customer checks, usage monitoring, and acceptable-use enforcement. These controls address the reuse path, and they can reduce the volume of reuse, but they cannot prevent it — a determined actor can establish a front, and the platform's controls are, in any case, jurisdictionally limited. The controls also do nothing for the jailbreak and clone paths, because those paths do not involve the platform.
Guardrails on agents. The developers can ship agents with guardrails that restrict their use. The guardrails address the direct use of the agent for prohibited purposes, but they are defeatable by jailbreak, and they do not survive the clone path — a cloned agent is run on the cloner's compute, where the developer's guardrails do not apply. The guardrails are, at best, a friction on the offensive use of the agent, and the friction is, for any actor with the sophistication to jailbreak or the access to a clone, zero.
Export controls on model weights. The regulators can impose export controls on the model weights, restricting their transfer to certain jurisdictions. The controls address the clone path, but only at the moment of first release — once the weights are in a jurisdiction, they can be copied within it and transferred from it, and the controls have no mechanism to prevent the secondary spread. The controls also do not address the open-source release, which is, by design, a transfer to all jurisdictions, and which is, in many cases, legal and encouraged.
Monitoring of offensive use. The defenders can monitor for the operational signature of the agent in the wild, and attribute its use to the actor who deployed it. This is a detection-and-attribution response, not a nonproliferation response — it does not prevent the spread of the agent; it responds to the agent's use. It is, in 2027, the most practical response, because it accepts that the agent will spread and focuses on the consequences. It is also the most expensive response, because it requires the defender to detect and attribute every operation conducted with every copy of the agent, and the volume of such operations is, by the design of the weapon, large.
None of these options addresses the structural problem: the weapon is a model plus a prompt, the model is infinitely copyable, and the prompt is infinitely shareable. The structural problem has no solution within the nonproliferation framework, because the framework was built for a world of scarce, expensive, factory-produced weapons, and the dual-use agent is none of those things.
Conclusion
The dual-use agent that walks out of the lab is the proliferation problem that the nonproliferation regime was not built to handle. The weapon is a model plus a prompt, not a factory, and the properties that make it a weapon — copyability, zero reproduction cost, no degradation, no signature, no latency — are the properties that defeat every control built for factory-based weapons. The agent reaches hostile actors through reuse, jailbreak, and clone paths, and each path exploits a different property of the agent's design. The defensive paradox — that the defender's demand for capability drives the development of the most dangerous weapons — has no resolution within the competitive market that produces the agents.
The implication is not that dual-use agents should not exist. They are, for the defender, a genuine advance, and their defensive value is real. The implication is that the proliferation of these agents is a fact to be adapted to, not a problem to be solved. The defensive posture of 2027 must assume that capable offensive agents are in the hands of every actor — state, criminal, and individual — and that the operations conducted with these agents will be, in volume and sophistication, what was once the province of a few advanced intelligence services. The defense that assumes a small number of capable adversaries is the defense that will be overwhelmed by a large number of them, each with the capability that was, a decade earlier, reserved for the few.
The lab is open. The door is wide. The agent is walking out. And the question for 2027 is not how to close the door — the door cannot be closed — but how to defend a world in which the weapon that was once a factory is now a file, and the file is in everyone's hands.
This dossier is part of the CyberArmory 2027 educational catalog. No live weapons are deployed. Every scenario is a controlled educational simulation designed to build pattern recognition and improve incident response readiness.
This report was compiled by the CyberArmory 2027 Research Collective as part of an educational dossier on speculative future cyber warfare technologies. No live weapons are deployed. Every scenario is a controlled educational simulation designed to build pattern recognition and improve incident response readiness.